
Home / Use cases / Enterprise-ready AI agent with SOC 2 and ISO 42001
SAAS & TECHNOLOGY
STARTUP
AI AGENTS
SOC 2 · ISO 42001
Enterprise-ready AI agent with SOC 2 and ISO 42001 for AI startups
An evaluation-gated contract-review agent, built with the controls enterprise buyers check. An evaluation-gated AI agent, SOC 2 and ISO 42001 controls, and a self-serve trust center.
Example engagement: figures show typical results for this kind of project.
3
frameworks built in: SOC 2, ISO 42001, trust center
5 mo
typical timeline, then ongoing
8
services working together
3
user roles, each with its own workspace
BUILT FOR
AI and SaaS startups selling to enterprises
INDUSTRY
SaaS & Technology
STAGE
Seed, 14 people
WHERE WE DELIVER
United States, Canada and Europe
TYPICAL TIMELINE
5 months, then ongoing
TEAM
Cross-practice: AI and data, security, software, strategy, managed cloud
Services used:
AI agents & automation
Generative AI & LLM apps
MLOps & LLMOps
SOC 2 compliance
AI governance & ISO 42001
SaaS & MVP development
Fractional CTO
Managed cloud
IN SHORT
How can an early-stage AI startup become enterprise-ready fast?
By treating AI quality, security and compliance as product features.
KEY TAKEAWAYS
→ Measure AI accuracy on a labelled evaluation set before buyers ask
→ Start SOC 2 early: Type II needs a 3-month observation window
→ Answer "do you train on our data?" in writing, with zero data retention
→ Route simple tasks to cheaper models to protect gross margin
THE CHALLENGE
Sound familiar?
The product demoed brilliantly. Then the first enterprise legal teams started asking hard questions.
01
A demo is not a product
AI accuracy often isn't measured. One prompt change can quietly break extraction, and nobody knows until a customer does.
02
Security reviews blocked every deal
Enterprise buyers send long security questionnaires and ask for SOC 2, SSO, data residency and a clear answer on AI training.
03
LLM costs were eating the margin
If LLM cost per document isn't managed, unit economics break at enterprise volumes, and investors notice.
TECHNICAL ARCHITECTURE
The whole product, in one picture
A multi-tenant SaaS with an agent layer behind an LLM gateway, so every model call is routed, cached, redacted, logged and evaluated.
USERS & CHANNELS
Legal workspace
Web app
Word add-in
Admin & trust settings
Web
Public API
REST + webhooks
↓
EDGE & ACCESS
CDN & WAF
API gateway
Rate limits per tenant
Identity
SAML SSO, SCIM, MFA
↓
CORE SERVICES
Workspaces & tenants
Document ingestion & OCR
Review workflows
Playbooks & rules
Billing & usage
↓
AI LAYER
Agent orchestrator
Plans and runs review steps
RAG over playbooks
Vector search
LLM gateway
Routing, caching, fallbacks
Guardrails
PII redaction, citation checks
Evaluation harness
A labelled set of real contracts
↓
DATA
PostgreSQL
Row-level security per tenant
Vector store
Encrypted object storage
Audit log
Analytics
↓
INTEGRATIONS
LLM providers
Zero data retention
E-signature
CRM
Slack & Teams
Customer SIEM
Audit export
SECURITY & COMPLIANCE
Across every layer
• SOC 2 controls, evidence automated
• ISO/IEC 42001 AI management system
• Row-level tenant isolation
• Zero data retention with model providers
• PII redaction before any LLM call
• Encryption with customer-managed keys
• SSO, SCIM and MFA
• Annual penetration test
THE SOLUTION IN DETAIL
One platform, three types of users
Legal teams review faster, customer admins stay in control, and the product team ships AI changes safely.
Product screens on this page show the design with sample data.
01
Legal teams
Legal workspace
6 core features
02
Customer admins
Admin & trust settings
6 core modules
03
Startup team
LLMOps & trust console
6 core modules
01
LEGAL WORKSPACE
Legal teams
In-house lawyers upload a contract and get an AI review against their own playbook in minutes, with redlines, explanations and the source clause for each.
CORE FEATURES
✓
AI contract review
Every clause checked against the customer's playbook.
✓
One-click redlines
Suggested wording from approved fallback positions.
✓
Explain source
Every finding links to the exact clause and rule.
✓
Playbook builder
Legal Ops define positions, fallbacks and severity.
✓
Review queue
Risk-ranked queue with owners and status.
✓
Word add-in
Review inside Microsoft Word, where lawyers work.
P
Paperline AI
LEGAL WORKSPACE
Inbox
Contracts
Review
Playbooks
Reports
Settings
MSA · Northbridge Logistics Ltd.
Vendor contract · 38 pages · reviewed by AI agent in 2 min 14 s · 7 issues found
Search contracts, clauses, counterparties…
Document
12.3 Limitation of liability
Supplier's aggregate liability shall not exceed the fees paid in the three (3) months preceding the claim.
14.1 Data protection
Supplier may process Customer Personal Data in any jurisdiction where it operates.
9.2 Payment terms
Customer shall pay undisputed invoices within sixty (60) days of receipt.
18.4 Auto-renewal
This Agreement renews automatically for successive 24-month terms unless terminated with 180 days notice.
AI review
7 issues · 2 high
High
Liability cap below playbook
Playbook requires 12 months of fees. Suggest: replace "three (3) months" with "twelve (12) months".
Apply redline
Explain source
High
Data transfers not restricted
GDPR: add SCCs and limit processing to approved regions (EU, UK).
Insert clause
Explain source
Medium
Auto-renewal notice too long
Playbook max: 90 days. Suggest 60 days.
Apply redline
Explain source
OK
Payment terms acceptable
60 days is within the approved range (30–60).
Accept
Explain source
AI review with issues and suggested redlines
P
Paperline AI
LEGAL WORKSPACE
Inbox
Contracts
Review
Playbooks
Reports
Settings
Vendor MSA playbook · v14
Rules the AI agent checks on every contract · owned by Legal Ops
Search contracts, clauses, counterparties…
Rules
CLAUSE
OUR POSITION
FALLBACK
SEVERITY
USED (30 D)
Limitation of liability
12 months of fees, mutual
6 months with VP approval
High
412
Data protection
EU/UK processing only, SCCs required
Approved subprocessors list
High
398
Auto-renewal
12-month terms, 60-day notice
90-day notice
Medium
356
Payment terms
30–60 days
90 days with CFO approval
Low
401
Indemnity
Mutual, IP and data breach
Capped at 2x fees
High
377
Governing law
England & Wales or Delaware
New York
Medium
389
Playbook rules
P
Paperline AI
LEGAL WORKSPACE
Inbox
Contracts
Review
Playbooks
Reports
Settings
Review queue
24 contracts this week · median AI review 2 min · 81% signed without escalation
Search contracts, clauses, counterparties…
In queue
24
Median AI review
2 min
−94%
Escalated to counsel
19%
Avg. turnaround
1.6 days
−5.4 days
Contracts
CONTRACT
COUNTERPARTY
TYPE
RISK
STATUS
OWNER
MSA v3
Northbridge Logistics
Vendor
High
In review
Priya (Legal)
DPA
Cloudmesh Inc.
Data
Medium
Redlines sent
Tom (Legal)
NDA
Halcyon Partners
NDA
Low
Auto-approved
AI agent
Order form
Brightwave Media
Sales
Low
Signed
Sales ops
SOW #7
Atlas Retail
Services
Medium
Waiting counterparty
Priya (Legal)
Risk-ranked review queue
02
ADMIN & TRUST SETTINGS
Customer admins
IT and security teams at each customer control identity, data residency and AI behaviour, and stream every action to their own SIEM.
P
Paperline AI
WORKSPACE ADMIN
Users & SSO
Security
AI & data
Audit log
Billing
AI & data controls
Workspace: Acme Corp legal · applies to all users
Search contracts, clauses, counterparties…
Data & model settings
Zero data retention
Model providers keep no prompts or outputs.
On
Never train on customer data
Contractually guaranteed in the DPA.
On
Data residency
EU (Frankfurt) region for all documents.
On
PII redaction before LLM
Names, emails and IDs masked automatically.
On
Allow external web search
Off for this workspace.
Off
Trust & compliance
SOC 2 Type II report
Issued 14 Oct 2026 · available under NDA
ISO/IEC 42001 readiness
AI management system in place · audit Q1 2027
Penetration test
0 critical, 0 high findings · Sep 2026
Subprocessors
6 listed · 30-day change notice
AI & data controls per workspace
P
Paperline AI
WORKSPACE ADMIN
Users & SSO
Security
AI & data
Audit log
Billing
Users & single sign-on
SAML SSO via Okta · SCIM provisioning on
Search contracts, clauses, counterparties…
Users
148
SSO
Okta SAML
SCIM sync
2 min ago
MFA
Enforced
Users
NAME
ROLE
TEAM
LAST ACTIVE
PROVISIONED
Priya Raman
Admin
Legal
4 min ago
SCIM
Tom Becker
Reviewer
Legal
1 h ago
SCIM
Sara Lind
Reviewer
Procurement
Today
SCIM
Mo Ahmed
Viewer
Finance
Yesterday
SCIM
Users, SSO and SCIM
P
Paperline AI
WORKSPACE ADMIN
Users & SSO
Security
AI & data
Audit log
Billing
Audit log
Every document access and AI action · exportable to your SIEM
Search contracts, clauses, counterparties…
Events
Streaming to Splunk
TIME
ACTOR
ACTION
OBJECT
RESULT
14:22:08
AI agent
Reviewed against playbook v14
MSA · Northbridge
Logged
14:21:40
Priya Raman
Uploaded document
MSA · Northbridge
Logged
13:58:12
Tom Becker
Applied 3 redlines
DPA · Cloudmesh
Logged
13:40:51
SCIM (Okta)
Deactivated user
j.doe
Logged
12:05:33
Unknown IP
Login attempt
—
Blocked
Audit log streaming to SIEM
CORE MODULES
✓
SSO & SCIM
Okta, Entra ID or Google, with automatic provisioning.
✓
AI & data controls
Zero retention, no training, PII redaction, region.
✓
Data residency
EU or US regions per workspace.
✓
Roles & permissions
Admin, reviewer and viewer roles.
✓
Audit log
Every document access and AI action, exportable.
✓
Trust documents
SOC 2 report, pen test summary and DPA on request.
03
LLMOPS & TRUST CONSOLE
Startup team
The founders and engineers see accuracy, cost and compliance in one place, and no AI change ships unless it passes the evaluation gate.
CORE MODULES
✓
Evaluation gate in CI
Every prompt, model or retrieval change tested first.
✓
Accuracy tracking
F1, recall and hallucinated citations per release.
✓
Cost & latency
Cost per contract by model, cache and route.
✓
Model routing
Cheaper models for simple steps, frontier models for hard ones.
✓
Guardrail monitoring
PII leaks and citation failures blocked and logged.
✓
Trust center
Public security page and questionnaire answer library.
P
Paperline AI
INTERNAL · LLMOPS
Evaluations
Cost & latency
Guardrails
Releases
Trust center
Evaluation runs
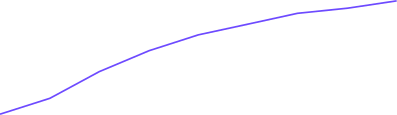
Every prompt, model or retrieval change is tested on 1,200 labelled contracts before release
Search contracts, clauses, counterparties…
Clause extraction F1
92.4%
+1.8
Issue detection recall
95.1%
+0.9
Hallucinated citations
0.3%
−0.4
Release gate
Passing
Accuracy over releases
Latest runs
v2.14 · new retrieval chunking
F1 92.4% · passed
v2.13 · prompt update
F1 90.6% · passed
v2.12 · cheaper model test
F1 84.1% · blocked
Evaluation runs gating every release
P
Paperline AI
INTERNAL · LLMOPS
Evaluations
Cost & latency
Guardrails
Releases
Trust center
Cost & latency
Model routing, caching and batching per task
Search contracts, clauses, counterparties…
Cost per contract
$0.71
−63%
p95 review time
2 min 40 s
−38%
Cache hit rate
41%
Monthly LLM spend
$9.8k
−51%
Cost per contract by month (USD)
Apr
May
Jun
Jul
Aug
Sep
Oct
Cost per contract by month
P
Paperline AI
INTERNAL · LLMOPS
Evaluations
Cost & latency
Guardrails
Releases
Trust center
Public trust center
trust.paperline.ai · 214 visits from buyer security teams this quarter
Search contracts, clauses, counterparties…
Certifications & reports
SOC 2 Type II
Clean opinion · Oct 2026
ISO/IEC 27001
Certification audit Feb 2027
ISO/IEC 42001
AI management system · readiness complete
Pen test summary
Sep 2026 · 0 critical
Security questionnaire answers
CAIQ v4
100%
SIG Lite
100%
AI model questionnaire
100%
Custom buyer questionnaires (avg)
87% auto-answered
Trust center & questionnaires
TECHNOLOGY & SECURITY
Built on a modern AI stack, secure by design
Chosen for fast iteration, measurable AI quality and enterprise trust.
TECHNOLOGY STACK
Frontend
Next.js
TypeScript
Office.js add-in
Backend
Python
FastAPI
PostgreSQL
pgvector
AI
Agent orchestration
Frontier + small models
LLM gateway
Prompt caching
LLMOps
Langfuse
Promptfoo
Evaluation sets
Cloud
AWS
ECS Fargate
S3 + KMS
Terraform
Compliance
Vanta
Okta
GitHub Actions
SECURITY & COMPLIANCE
✓ SOC 2 Type II, evidence collected automatically
✓ ISO/IEC 42001 AI management system readiness
✓ Zero data retention agreements with model providers
✓ No training on customer data, written into the DPA
✓ PII redaction before any model call
✓ Row-level tenant isolation with customer-managed keys
✓ SSO, SCIM and enforced MFA
✓ Annual penetration test with fixes verified
DELIVERY TIMELINE
From demo to enterprise-ready in about 5 months
Product, AI quality and compliance run in parallel, so the SOC 2 observation window can start early.
Month 0
Month 1
Month 2
Month 3
Month 4
Month 5
Architecture & fractional CTO
Target architecture, security baseline, roadmap.
Wk 0–2
Evaluation harness & agent rebuild
Labelled evaluation set from real contracts, agent redesign.
Wk 2–10
Enterprise features
SSO, SCIM, roles, tenant isolation, audit log.
Wk 4–12
SOC 2 readiness
Policies, controls and automated evidence.
Wk 2–10
SOC 2 observation period
Controls operating; Type II audit window.
Wk 10–22
LLM gateway & cost control
Routing, caching and batching.
Wk 8–16
ISO 42001 readiness & launch
AI policy, risk assessment, trust center live.
Wk 14–22
Typical plan: about 5 months to SOC 2 and enterprise launch
An AI product that answers security and AI reviews with evidence, not promises. An evaluation-gated AI agent, SOC 2 and ISO 42001 controls, and a self-serve trust center.
WHAT THIS USE CASE DELIVERS
Use case blueprint. Scope, timeline and team are confirmed in a written proposal for your project.
RELATED USE CASES
More work like this
FINTECH
AI agents
DORA
Agentic AI KYC, real-time fraud scoring and DORA for payments fintechs
THE CHALLENGE
Onboarding, fraud and new DORA rules pulling the business in different directions.
OUR APPROACH
Agentic AI for KYC, real-time fraud scoring and DORA resilience testing.
WHAT SUCCESS LOOKS LIKE
Faster, consistent onboarding decisions with people in the loop, and DORA evidence ready.
3
workstreams: KYC agents, fraud, DORA
Read the story →
1 / 3
RELATED INDUSTRIES
Built for your industry
The industry behind this use case, and others where the same approach works.
All industries →
BLOG & RESOURCES
Insights for SaaS and technology leaders
Practical guides on compliance, AI features and scaling your platform.
View all resources →
COMPLIANCE
SOC 2 for SaaS: unblock enterprise security reviews
The controls, reports and trust-center answers buyers check.
Akash Soni, Founder & CEO · 8 min read
AI FOR SAAS
AI features for SaaS: what enterprise buyers now expect
Guardrails, evaluation and data-use terms that pass review.
Akash Soni, Founder & CEO · 8 min read
AI AGENTS
AI agents: how to pick the first processes to automate
A scoring method, guardrails and the metrics that prove value.
Akash Soni, Founder & CEO · 9 min read
FAQ
AI startup and SOC 2 questions, answered
Short answers to what teams ask us most about this kind of project.

Still have a question?
Book a free consultation

How long does SOC 2 take for an AI startup?
An AI startup on modern cloud tooling can be ready for a SOC 2 Type I audit in 8 to 12 weeks and complete a first Type II within about 5 to 9 months, depending on the observation period. Adding AI-specific controls early avoids rework.
What is ISO/IEC 42001?
ISO/IEC 42001 is the international standard for an AI management system. It requires AI risk and impact assessments, data and model controls, human oversight and monitoring, and lets AI companies prove responsible AI to enterprise buyers through certification.
How do you measure LLM accuracy?
We build an evaluation set of real, labelled examples and score each release on accuracy metrics such as F1, groundedness, citation correctness and refusal behaviour. A release only ships if it meets the agreed target.
How can we reduce LLM costs?
Route simple tasks to smaller models, cache repeated results, trim prompts and retrieved context, batch where possible and monitor cost per request.
Do enterprise buyers need SSO?
Almost always. Enterprise security teams expect SAML or OIDC single sign-on, SCIM user provisioning, role-based access and audit logs before approving a SaaS vendor.
SERVICES IN THIS USE CASE
AI Agent Development & Workflow Automation →
AI agents that finish real work
Generative AI & LLM Application Development →
LLM and RAG apps built for production
MLOps & LLMOps Services →
Run models in production at a known cost
SOC 2 Compliance & Audit Readiness →
Pass your SOC 2 audit and unblock enterprise deals
Building an AI product for enterprise buyers? Let's talk.
Book a free 30-minute call. You'll leave with what your buyers will ask for and a realistic plan to get there, whether or not we work together.

What buyers will ask for
A realistic plan
No obligation