
Home / Use cases / PCI DSS 4.0 and unified compliance
ECOMMERCE & RETAIL
ENTERPRISE
PCI DSS 4.0
UNIFIED COMPLIANCE
PCI DSS 4.0 and unified compliance for multi-market retailers
Payment-page script control and one control framework across stores, eCommerce and markets. Checkout script control plus one unified control framework across every market.
Example engagement: figures show typical results for this kind of project.
5
frameworks mapped to one control set
7 mo to PCI DSS 4.0
typical timeline
8
services working together
3
user roles, each with its own workspace
BUILT FOR
Multi-market retailers taking card payments
INDUSTRY
eCommerce & Retail
TYPICAL SIZE
Mid-size to enterprise
WHERE WE DELIVER
United States, Canada and Europe
TYPICAL TIMELINE
7 months to PCI DSS 4.0
TEAM
Cross-practice: security, managed cloud, strategy
Services used:
Cloud & application security
Penetration testing
ISO 27001 certification
GDPR & data privacy
SOC 2 compliance
SOC as a Service
Vulnerability & patching
IT architecture assessment
IN SHORT
What changed in PCI DSS 4.0 for eCommerce checkout pages?
Since 31 March 2025, requirements 6.4.3 and 11.6.1 are mandatory: every script on a payment page must be authorised, justified and integrity-checked, and unauthorised changes to payment pages must be detected.
KEY TAKEAWAYS
→ Inventory every script on payment pages and justify each one
→ Detect payment page changes at least weekly; we scan every 15 minutes
→ Map controls once and reuse evidence across frameworks
→ Stop card testing at the edge, before it reaches checkout
THE CHALLENGE
Sound familiar?
A growing online business, a large store estate and a new version of PCI DSS with deadlines that could not move.
01
Checkout skimming risk
Marketing and vendor scripts often run on checkout pages with no inventory, the exact gap PCI DSS 4.0 requirements 6.4.3 and 11.6.1 target.
02
Card-testing bots and chargebacks
Bots test stolen cards against checkout at scale, driving chargebacks and payment processor penalties.
03
Five frameworks, five spreadsheets
When PCI DSS, ISO 27001, SOC 2, GDPR and NIS2 run separately, teams answer the same auditor questions again and again.
TECHNICAL ARCHITECTURE
How the protection fits together
Controls sit at the edge, in the browser and in the compliance layer, so a malicious script is blocked, detected and evidenced without slowing checkout.
USERS & CHANNELS
Web stores in every market
Headless
Mobile apps
iOS & Android
Stores across markets
POS terminals
Marketplace partners
APIs
↓
EDGE
CDN & WAF
Bot management
Card-testing defence
CSP & SRI headers
Script allow-listing
↓
COMMERCE SERVICES
Checkout
Payments
Tokenized iframe fields
Accounts & loyalty
Orders
Promotions
↓
SECURITY CONTROLS
Script inventory & approvals
PCI DSS 6.4.3
Tamper detection
PCI DSS 11.6.1, every 15 min
Checkout fraud scoring
Secrets & key management
↓
DATA & EVIDENCE
Card vault
At payment provider
Customer data platform
Logs to SIEM
Evidence library
Reused across audits
↓
GRC & INTEGRATIONS
GRC platform
One unified control library
Ticketing
Payment provider
Auditor portal
QSA & ISO
SECURITY OPERATIONS
Across every layer
• 24/7 SOC with fast containment
• Quarterly ASV scans
• Annual pen test and segmentation tests
• MFA for all cardholder data access
• POS networks segmented per store
• Vendor risk reviews for every supplier
• Incident playbooks incl. NIS2 24 h warning
• Board reporting every quarter
THE SOLUTION IN DETAIL
One programme, three teams
Security engineers control the checkout, compliance runs one framework, and leadership sees risk in business terms.
Product screens on this page show the design with sample data.
01
Security & payments
Payment page protection
6 core modules
02
Compliance team
Unified control framework
6 core modules
03
Leadership & CISO
Risk dashboard
6 core modules
01
PAYMENT PAGE PROTECTION
Security & payments
AppSec and payments engineers know every script on every checkout page, approve changes with a reason, and get an alert within minutes if anything changes.
CORE MODULES
✓
Script inventory
Every script on every checkout page, with owner and purpose.
✓
Approval workflow
Business justification recorded for PCI DSS 6.4.3.
✓
Integrity checks
Subresource integrity and Content Security Policy.
✓
Tamper detection
Page and header changes detected for PCI DSS 11.6.1.
✓
Bot & card-testing defence
Automated attempts blocked at the edge.
✓
Checkout fraud scoring
Risky orders stepped up or held.
N
Northcrest Retail
SECURITY & PAYMENTS
Payment pages
Bot & fraud
Controls
Markets
Vendors
Risk
Checkout script inventory
PCI DSS 4.0 req. 6.4.3 · 214 checkout pages across 12 markets · scanned every 15 min
Search controls, scripts, vendors, markets…
Scripts on payment pages
37
Authorised & justified
35
Blocked this month
2
Integrity checks
Passing
Scripts
SCRIPT
SOURCE
PURPOSE
INTEGRITY
APPROVED BY
STATUS
checkout-core.js
First party
Checkout logic
SRI hash
AppSec
Approved
payments-sdk.js
Payment provider
Card fields (iframe)
SRI hash
Payments
Approved
tag-manager.js
Marketing vendor
Analytics
Restricted
CISO
Approved · sandboxed
chat-widget.js
Support vendor
Customer chat
SRI hash
AppSec
Approved
cdn-fonts-x9.js
Unknown domain
Unknown
No hash
—
Blocked
Checkout script inventory
N
Northcrest Retail
SECURITY & PAYMENTS
Payment pages
Bot & fraud
Controls
Markets
Vendors
Risk
Change & tamper detection
PCI DSS 4.0 req. 11.6.1 · HTTP headers and page content monitored on every checkout
Search controls, scripts, vendors, markets…
Alerts this week
New script injected · checkout DE
Unknown domain, blocked in 40 s, incident opened
CSP header changed · checkout UK
Approved change, release 4.18
Payment iframe source changed
Provider update, verified
Skimmer signature match · test store
Red team exercise, contained
Checks per day
Mon
Tue
Wed
Thu
Fri
Sat
Sun
Change & tamper detection
N
Northcrest Retail
SECURITY & PAYMENTS
Payment pages
Bot & fraud
Controls
Markets
Vendors
Risk
Bots, card testing & account takeover
Edge bot management + fraud scoring at checkout
Search controls, scripts, vendors, markets…
Bot requests blocked (24 h)
4.2M
Card-testing attempts
18,940
−97%
Chargeback rate
0.21%
−0.38 pts
False positives
0.04%
Card-testing attempts per day
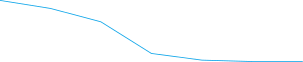
Card-testing defence
02
UNIFIED CONTROL FRAMEWORK
Compliance team
One control library covers PCI DSS, ISO 27001, SOC 2, GDPR and NIS2, so evidence is collected once and reused in every audit and every market.
N
Northcrest Retail
COMPLIANCE
Payment pages
Bot & fraud
Controls
Markets
Vendors
Risk
Unified control framework
612 controls mapped once to PCI DSS 4.0, ISO 27001, SOC 2, GDPR and NIS2 · evidence collected automatically
Search controls, scripts, vendors, markets…
Controls
612
Evidence automated
78%
+61 pts
Overdue evidence
6
Frameworks covered
5
Controls
CONTROL
FRAMEWORKS
OWNER
EVIDENCE
STATUS
MFA for all admin access
PCI 8.4 · ISO A.5.17 · SOC 2 CC6.1
IAM
Automated
Effective
Payment page script control
PCI 6.4.3 · 11.6.1
AppSec
Automated
Effective
Vendor risk assessment
ISO A.5.19 · NIS2 Art. 21 · GDPR 28
Procurement
Quarterly
Effective
Data retention & deletion
GDPR 5(1)(e) · ISO A.8.10
Privacy
Automated
Effective
Log review & alerting
PCI 10.4 · SOC 2 CC7.2
SOC
Automated
Effective
Annual pen test
PCI 11.4 · ISO A.8.8
AppSec
Report
Due Dec
Unified control framework
N
Northcrest Retail
COMPLIANCE
Payment pages
Bot & fraud
Controls
Markets
Vendors
Risk
Compliance by market
12 markets · local privacy and payment rules tracked
Search controls, scripts, vendors, markets…
Markets
United Kingdom · PCI DSS, UK GDPR
Compliant
Germany · PCI DSS, GDPR, NIS2
Compliant
France · PCI DSS, GDPR
Compliant
United States · PCI DSS, CCPA/CPRA
Compliant
India · PCI DSS, DPDP Act
Consent flows rolling out
UAE · PCI DSS, PDPL
Data mapping in progress
Compliance by market
N
Northcrest Retail
COMPLIANCE
Payment pages
Bot & fraud
Controls
Markets
Vendors
Risk
Audit evidence
QSA and ISO auditor requests · answered from one evidence library
Search controls, scripts, vendors, markets…
Open requests
14
Answered from library
91%
Avg. turnaround
1.2 days
was 9 days
Audit findings
0 major
Requests
REQUEST
AUDITOR
CONTROL
EVIDENCE
STATUS
Show 6.4.3 script authorisations
QSA
PCI 6.4.3
Script inventory export
Sent
MFA coverage for admins
QSA
PCI 8.4
IdP report, auto
Sent
Supplier security reviews
ISO auditor
A.5.19
Vendor register
In review
Incident response test
ISO auditor
A.5.24
Tabletop report
Sent
Data retention evidence
DPO
GDPR 5(1)(e)
Deletion job logs
Due Fri
Audit evidence requests
CORE MODULES
✓
One unified control library
Mapped once to five frameworks.
✓
Automated evidence
Evidence collected automatically wherever possible.
✓
Market tracker
Local rules for every market in one view.
✓
Auditor requests
Answered from the evidence library in about a day.
✓
Policy management
Policies versioned, approved and acknowledged.
✓
Exceptions
Risk acceptances with expiry dates.
03
RISK DASHBOARD
Leadership & CISO
The CISO and board see compliance status, top risks, third parties and incident trends in plain business terms, every day.
CORE MODULES
✓
Board risk dashboard
Status, top risks and owners.
✓
Audit calendar
PCI DSS, ISO 27001 and SOC 2 milestones.
✓
Third-party risk
Every vendor, flagged by access to sensitive data.
✓
Incident trends
Detection and containment times.
✓
Roadmap & budget
Security investments tied to risk reduction.
✓
Quarterly board pack
Generated from live data.
N
Northcrest Retail
EXECUTIVE
Payment pages
Bot & fraud
Controls
Markets
Vendors
Risk
Security & compliance risk
Board view · updated daily
Search controls, scripts, vendors, markets…
PCI DSS 4.0 status
Compliant
Critical vulns > 15 days
0
Third parties high risk
4
Mean time to contain
22 min
Top risks
Marketing tags on payment pages
Sandboxed, review monthly
Legacy POS in 40 stores
Segmented, replacement Q2
Vendor with weak MFA
Remediation plan agreed
Audit calendar
PCI DSS ROC (QSA)
Passed · Sep 2026
ISO 27001 surveillance
Passed · Oct 2026
SOC 2 Type II (marketplace)
Window ends Dec
CISO risk dashboard
N
Northcrest Retail
EXECUTIVE
Payment pages
Bot & fraud
Controls
Markets
Vendors
Risk
Third-party risk
186 vendors · 42 with access to customer or payment data
Search controls, scripts, vendors, markets…
High-impact vendors
VENDOR
SERVICE
DATA ACCESS
ASSESSMENT
RISK
ACTION
Payment provider
Card processing
Card data (tokenized)
Oct 2026
Low
Annual review
Marketing tag vendor
Analytics
Browsing data
Sep 2026
Medium
Sandboxed on checkout
Logistics partner
Deliveries
Names, addresses
Aug 2026
Medium
MFA rollout agreed
Support platform
Customer chat
Order data
Oct 2026
Low
Annual review
Third-party risk
N
Northcrest Retail
EXECUTIVE
Payment pages
Bot & fraud
Controls
Markets
Vendors
Risk
Incidents & response
24/7 SOC across 1,140 stores, 4 DCs and 12 web stores
Search controls, scripts, vendors, markets…
Incidents (quarter)
63
Customer-impacting
0
Mean time to detect
6 min
Mean time to contain
22 min
Mean time to contain (minutes)
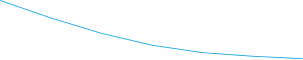
Incidents & response
TECHNOLOGY & SECURITY
Built from proven security and compliance tooling
Edge, browser, detection and GRC layers working together.
TECHNOLOGY STACK
Edge
CDN & WAF
Bot management
CSP & SRI
Detection
Script monitoring
SIEM
SOAR
GRC
GRC platform
Evidence automation
Ticketing
Identity
SSO
MFA
Privileged access
Cloud
AWS
Azure
Testing
ASV scans
Penetration testing
Red team
SECURITY & COMPLIANCE
✓ PCI DSS 4.0 requirements 6.4.3 and 11.6.1 met
✓ Quarterly ASV scans and annual penetration tests
✓ POS networks segmented and tested
✓ MFA for all cardholder data environment access
✓ One control set for PCI DSS, ISO 27001, SOC 2, GDPR, NIS2
✓ Vendor risk reviews for every supplier
✓ 24/7 SOC with fast containment
✓ NIS2 incident playbooks with 24 h early warning
DELIVERY TIMELINE
From gap analysis to PCI DSS 4.0 in about 7 months
Checkout risk first, then the unified framework, then the audits.
Month 0
Month 1
Month 2
Month 3
Month 4
Month 5
Month 6
Month 7
Assessment & gap analysis
Scope, scripts, controls and markets.
Wk 0–4
Script inventory & approvals
Every checkout script found, justified, approved.
Wk 3–10
Tamper detection & CSP
Monitoring on every payment page, alerts to the SOC.
Wk 6–14
Bot & fraud defence
Edge bot management, checkout fraud scoring.
Wk 8–16
Unified control framework
Controls mapped once, evidence automated.
Wk 4–22
QSA assessment & ISO audit
Report on Compliance, ISO surveillance.
Wk 22–28
Managed compliance & SOC
Continuous monitoring and evidence.
Wk 26–30
Typical plan: about 7 months to PCI DSS 4.0 readiness
One set of controls and evidence for PCI DSS, ISO 27001, SOC 2 and privacy audits. Checkout script control plus one unified control framework across every market.
WHAT THIS USE CASE DELIVERS
Use case blueprint. Scope, timeline and team are confirmed in a written proposal for your project.
RELATED USE CASES
More work like this
FINTECH
AI agents
DORA
Agentic AI KYC, real-time fraud scoring and DORA for payments fintechs
THE CHALLENGE
Onboarding, fraud and new DORA rules pulling the business in different directions.
OUR APPROACH
Agentic AI for KYC, real-time fraud scoring and DORA resilience testing.
WHAT SUCCESS LOOKS LIKE
Faster, consistent onboarding decisions with people in the loop, and DORA evidence ready.
3
workstreams: KYC agents, fraud, DORA
Read the story →
1 / 3
RELATED INDUSTRIES
Built for your industry
The industry behind this use case, and others where the same approach works.
All industries →
BLOG & RESOURCES
Insights for commerce and retail teams
Practical guides on speed, AI and peak-season readiness.
View all resources →
PAYMENTS
PCI DSS scope reduction: protect card data by never touching it
Hosted fields, tokenization and segmentation, explained.
Krima Soni, CFO · 8 min read
PEAK SEASON
Black Friday readiness: load tests, code freezes and on-call
A 10-week plan for peak traffic, bots and fraud.
Akash Soni, Founder & CEO · 8 min read
PENETRATION TESTING
How to scope a penetration test and fix what matters first
Test types, grey vs black box and reading the report.
Akash Soni, Founder & CEO · 8 min read
FAQ
PCI DSS 4.0 and retail compliance questions, answered
Short answers to what teams ask us most about this kind of project.

Still have a question?
Book a free consultation

What are PCI DSS 4.0 requirements 6.4.3 and 11.6.1?
Requirement 6.4.3 requires merchants to authorize, justify and check the integrity of every script on payment pages. Requirement 11.6.1 requires detecting unauthorized changes to payment pages and their HTTP headers. Both became mandatory on 31 March 2025.
What is e-skimming (Magecart)?
E-skimming, often called Magecart, is when attackers inject malicious JavaScript into checkout pages to steal card details as customers type. Script control and change detection under PCI DSS 4.0 are designed to stop it.
How do you stop card-testing attacks?
Combine bot management, rate limiting, CAPTCHA on risky patterns, velocity rules, fraud scoring and monitoring of payment declines.
Can one set of controls cover several frameworks?
Yes. A unified control framework maps one control to PCI DSS, ISO 27001, SOC 2 and privacy laws at once, so teams implement and evidence it once, cutting audit effort across markets.
How often must payment pages be checked for changes?
PCI DSS 4.0 requirement 11.6.1 requires checking payment pages for unauthorized changes at least weekly, or at a frequency set by your targeted risk analysis. Many retailers monitor continuously.
SERVICES IN THIS USE CASE
Cloud & Application Security →
Secure cloud setup and code before release
Penetration Testing (VAPT) →
Find what attackers would find, first
ISO 27001 Certification Consulting →
Build your ISMS and certify first time
GDPR & Data Privacy Compliance →
GDPR, CCPA and DPDP privacy programs
Getting ready for your next PCI DSS assessment? Let's talk.
Book a free 30-minute call. You'll leave with your biggest PCI DSS 4.0 gaps and how to close them, whether or not we work together.

Your biggest PCI DSS gaps
How to close them
No obligation